LandOffer
Workplace Communication
How to Disagree with a Technical Decision and Still Help the Team Move Forward
A complete fictional objection rewrite and prototype decision record compare evidence and alternatives, retain dissent, and define next commitments and revisit conditions.
Disagree with a technical decision by naming the shared goal, the specific risk, the evidence behind it, and a workable alternative with its own costs. Ask the decision owner what would change the choice. Once a decision is made, record the trade-off, your contribution to the chosen path, and the conditions for reviewing it again. You can support execution without claiming that your concern disappeared.
The useful output is an actionable decision with an explicit rationale and a way to examine its assumptions. This LandOffer.ai guide works through a fictional technical objection, its rewrite, and a completed decision record. The case ends with an agreed prototype direction and validation gates; no code, benchmark, recovery behavior or production outcome has been tested.
Establish what is being decided and who owns it
Before arguing about a solution, identify the decision's scope. Are you choosing a prototype direction, approving an architecture, or authorizing a release? Those are different commitments. A team may accept a direction for investigation without accepting its untested behavior as safe to ship.
Ask which requirements and constraints matter now, who owns the decision, and which affected people need input. If ownership is unclear, resolve that before treating the most persistent commenter as the final authority. You can disagree with the decision owner's reasoning without inventing authority for yourself.
AWS's architectural decision-record guidance recommends recording the decision, context and consequences, with an identified owner and decision status. That provides a useful structure for significant choices. It does not mean every workplace conversation needs a formal architecture document or that a written record creates approval authority.
In the fictional case, a desktop scientific-image viewer needs offline search over annotations. Kenji owns the technical direction. Brielle proposes moving index work into a separate local worker. Luca will build the approved prototype. Product owner Ines owns the search scope; release owner Tessa will decide release readiness through the team's normal process.
Replace a verdict with a reviewable objection
The initial proposal reuses the viewer's existing embedded-index component for a prototype. Brielle writes: “Putting this in the app is a bad architecture. We will regret it when the projects get bigger. We should use a worker.” That communicates a preference, but it does not explain which condition threatens the goal or what the alternative would require.
The team has three explicit case facts: search must work offline; the first proposed scope indexes a static annotation snapshot rather than live updates; and the existing embedded component is already included in the team's application package. These are invented scenario constraints, not verified properties of a real product or claims about a particular vendor library.
Brielle rewrites the objection into a completed memo:
Shared goal: provide offline annotation search while keeping the viewer usable during index creation. I agree that the first scope can use a static snapshot.
Concern: the current proposal does not explain how indexing is scheduled or cancelled while users interact with the viewer. Reusing an embedded component does not, by itself, establish responsiveness or safe recovery after interruption.
Evidence and uncertainty: the proposal names the component and snapshot input, but leaves the execution boundary and interruption behavior unspecified. I have not measured indexing time, UI responsiveness or restart behavior. My concern is a design gap to resolve, not a demonstrated failure or a claim that larger projects already break the application.
Alternative: prototype index creation in a separate local worker with an explicit request, cancellation and completion contract. This preserves the offline requirement but adds process-lifecycle, packaging and failure-handling work that we have not scoped or validated.
Evidence against my preference: the embedded component is already packaged, and the static-snapshot scope may allow a simpler bounded design. A separate worker is not automatically reliable or easy to reverse. I am willing to support the embedded prototype if we define the scheduling, interruption and validation gates before implementation begins.
Decision requested: Kenji, can we choose the prototype direction after comparing those costs, and record which results would require revisiting it before any release approval?
Kenji can now answer a concrete question about execution and validation boundaries instead of defending an entire architecture against a verdict. It preserves the counterargument and the limits of the evidence. It also changes an unsupported prediction about future failure into a question the prototype can investigate.
Compare alternatives against the same requirements
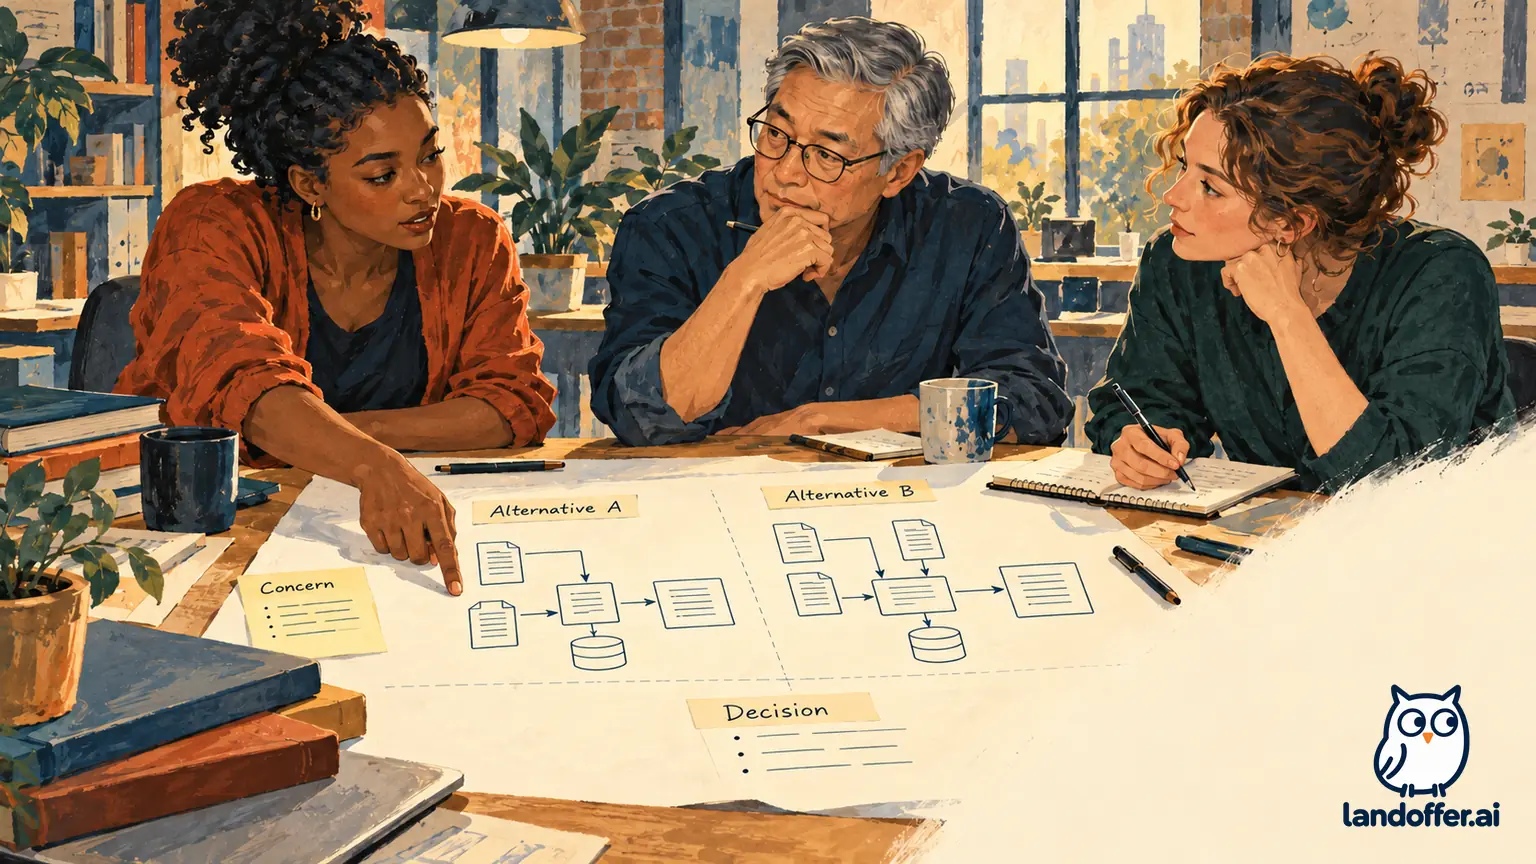
Compare both options against the same requirements, including the unfinished work in your preferred approach. Give both the same requirements and identify the extra work each one creates. In this example, offline operation applies to both options; neither can be rejected merely for requiring a network because both proposals are local.
| Decision factor | Reuse embedded component for the prototype | Separate local-worker prototype |
|---|---|---|
| Current package | Existing component is already included under the case assumptions | Additional worker lifecycle and packaging need a design |
| Execution boundary | Scheduling, cancellation and UI interaction still need to be specified | Request, cancellation and completion contract still need to be specified |
| Failure handling | Interrupted build and restart behavior untested | Worker failure, partial output and restart behavior untested |
| Current scope | Static annotation snapshot only | Same static snapshot only; live updates are outside both options |
| Reversibility | Need an explicit output boundary before assuming replacement is easy | Need an explicit output boundary before assuming replacement is easy |
This comparison does not produce a measured winner. It establishes what Kenji is trading off and what neither approach has proved. “A worker isolates the concern” is not a substitute for examining what happens when that worker fails or the application closes.
Microsoft's architecture decision-record guidance recommends including options, trade-offs, confidence, status and rationale. That encourages a record that can be questioned later with relevant evidence. It does not establish that either option in this fictional comparison has better performance or lower risk.
If more evidence is needed before a choice, propose a bounded investigation with an owner and endpoint. Avoid asking for an unlimited research project merely to postpone a decision you dislike. Also avoid calling a concern “just a preference” when it identifies a material requirement that the proposal has not addressed.
A completed decision record with retained dissent
Kenji chooses the embedded-component prototype after reviewing the memo with Brielle, Luca and Ines. The following is the completed fictional record. Its accepted status concerns prototype direction only, not implementation completeness, a validated architecture or permission to deploy.
Decision and owner: Kenji accepts reuse of the existing embedded component for a bounded offline, static-snapshot annotation-search prototype. Ines confirms that live updates are outside the current product scope. Tessa retains release authority.
Reason: this direction uses the component already in the scenario's application package and limits the first investigation to one snapshot. The team is avoiding unscoped worker-lifecycle work at this stage, not claiming that the embedded approach has passed responsiveness or recovery checks.
Alternative not selected now: a separate local worker remains a credible option. It introduces a process contract and packaging work requiring its own scope. No worker implementation or comparative benchmark exists in this case.
Retained disagreement: Brielle prefers an explicit worker boundary because scheduling and interruption behavior remain unresolved. She accepts the prototype decision as a bounded investigation while retaining that concern in the record. Kenji owns the choice and the rationale; the record does not imply unanimous architectural preference.
Before prototype implementation: Luca will write the proposed scheduling, cancellation and output-validity boundaries. Brielle will review those questions within the agreed review time. Kenji must approve that bounded design before implementation starts. Unspecified behavior is not treated as already solved.
Validation before release consideration: the team will use approved project fixtures to examine interaction during index creation, cancellation, interrupted builds and restart behavior against criteria agreed by Kenji and Tessa before testing. Record the environment, cases, observed behavior and limits. No validation has yet occurred; no release is authorized by this record.
Revisit conditions: return to Kenji if the proposed design cannot define a workable interruption or output-validity boundary, or if later validation fails an agreed responsiveness, cancellation or restart criterion. A new live-update requirement also reopens the scope. A critical safety or security issue follows the appropriate immediate escalation route rather than waiting for a routine checkpoint.
Commitments and checkpoint: Luca owns the design proposal; Brielle owns the bounded review; Kenji owns the next decision. Review the design on November 6, 2026. If the evidence changes the direction, preserve this rationale and create a linked superseding decision rather than rewriting the original disagreement away.
The fictional record authorizes the next design step while leaving implementation, validation and release unresolved. There is an owner for the next work, a decision before implementation, and a later release boundary. The date is a fictional planning commitment, not a promised delivery or proof of readiness.
Commit to a useful action after the decision
Brielle's completed response to Kenji is: “I still prefer the worker boundary, but I understand the chosen prototype scope and its limits. I will review Luca's scheduling and interruption proposal, identify any unresolved requirement, and help define the validation cases. I will use the recorded revisit conditions rather than reopen the same preference in every discussion.”
That is a concrete commitment. It does not require Brielle to tell others she thinks the embedded option is best. When explaining the direction, she can accurately describe the team's decision and rationale while distinguishing it from her preference. She should flag any proposed departure from the recorded scope to Kenji before building a different approach.
GitLab's communication handbook describes its expectation that people disagree, commit and advocate after a decision in its collaborative process. Treat that as a named company's practice, not a universal obligation to suppress concerns or ignore another employer's escalation rules. Supporting the next agreed step can coexist with an accurate record of disagreement.
If you cannot carry out a commitment because it conflicts with a responsibility or material risk, say so promptly and use the appropriate owner or escalation route. Silent noncompliance and repeated vague objections make it harder to distinguish an unresolved requirement from a disagreement already considered.
Reopen the question when the evidence changes
Write the observation that triggers review and name the decision owner who will assess its implications. “If this becomes problematic” is too vague. In the case, an unresolved interruption boundary or a failed agreed validation criterion provides a reason to return to Kenji. A preference that was already recorded, without new evidence, does not by itself create a new decision.
Separate a triggered review from a predetermined reversal. A failed criterion might lead to a narrower scope, a revised embedded design, a worker investigation, or a decision to stop. The owner must examine the result and the available alternatives. A triggered review requires a new reasoned decision; it does not preselect the worker alternative.
Keep the evidence and status legible. Prototype acceptance is not release acceptance. A proposed worker is not an implemented fallback. A plan to test recovery is not tested recovery. If a later direction supersedes the first, preserve the original context so future colleagues can understand why the choice changed.
Leave the team with a decision and a next step
Before raising your objection, write the requirement at risk, the evidence you have, what you do not know, and an alternative with its costs. Ask the owner for a decision at the right scope. Afterward, record the rationale, remaining concern, next contribution and conditions that justify another review.
You do not need to agree with every technical preference to help the team act responsibly. You do need an accurate account of what was decided, which uncertainties remain, and what you will do next. For more practical workplace guides, visit LandOffer.ai.