LandOffer
Job search
Data Governance Portfolio: Connect a Business Glossary to Lineage and Access Decisions
Connect a synthetic glossary to executed SQLite lineage and a conditional use decision, with counterexamples that expose the enforcement boundary.
A data governance portfolio should let a reviewer follow a business term into the data it describes, identify who is responsible for it, and understand why a proposed use was accepted or refused. A glossary spreadsheet and an attractive lineage diagram are useful starting points. A reviewer should be able to check a use decision against the actual fields and transformations, rather than infer governance from the diagram alone.
This guide builds and executes an original synthetic SQLite example, then evaluates a separate data-use request against an authored policy. It does not operate Microsoft Purview, represent a real organization, obtain a person's approval, or grant database permissions. The distinction between a documented decision and an enforced restriction is part of the finished evidence.
Use LandOffer’s recently posted jobs to identify the stewardship, catalog, lineage, or access-review responsibility your sample should demonstrate. Keep the case small enough that a reviewer can trace every important relationship.
Give the catalog a business question
The fictional service-operations team wants a regional summary of closed support tickets for capacity planning. It does not need contact details for that purpose. The portfolio therefore asks two connected questions: what does the summary mean, and what use of it would the proposed governance policy permit?
Four invented tickets provide a manageable dataset. Each has a synthetic identifier, an address under the reserved .invalid domain, a region, recorded minutes, and a state. These are authored examples rather than anonymized records from a real service desk. Recorded minutes are fixture values, not measured resolution durations.
The business term resolution_minutes means recorded minutes for closed tickets only. Open-ticket duration is excluded. The related regional_closed_summary means a per-region count and total of those minutes. Neither definition establishes a service-level agreement, a performance rating, or an industry-standard measure.
Name the role responsible for meaning before describing who would implement access. This example names fictional business-owner, data-steward, and access-provider roles. The business owner is accountable for the proposed meaning, the steward reviews its catalog representation, and the provider would implement an approved access change. Those descriptions do not claim that real people have accepted the responsibilities.
Connect terms to fields, not just dataset names
The current Microsoft Purview glossary guidance describes linking business terms to products, assets, columns, and critical data elements, with policy context attached to terms. It also explains that governance domains can distinguish meanings used by different parts of an organization. This is documentation context; no Purview catalog was configured for this article.
A local sample can demonstrate a narrower, inspectable version of that reasoning. Store the term identifier, definition, responsible role, and specific target column together. If the definition says closed tickets, the implementation must show where the state filter occurs. That connection lets a reviewer locate the filter that implements the term; a database-wide label would leave the relevant field and rule ambiguous.
Keep classification and permission separate. The source contains synthetic contact-like fields, the intermediate relation contains synthetic operational rows, and the final relation contains aggregates. Those labels describe the fixture's structure. They do not establish that aggregation anonymizes real people, that a legal basis exists, or that any particular user is authorized.
A useful catalog also says how its links were established. Here, column mappings were authored and checked against SQLite schemas. They were not discovered by a scanner or inferred automatically from SQL. That distinction helps a reviewer assess what the evidence actually covers.
Asset one: a completed catalog and checked lineage
The first completed asset contains three data assets, two business terms, three fictional owner roles, and two directed lineage edges. The original script creates the database, inserts the fixture, executes the views, and saves the catalog and results. The following inventory corresponds to those executed relations.
| Asset | Actual fields and grain | Definition and responsibility |
|---|---|---|
| tickets | ticket_id, email, region, minutes, state; one synthetic ticket per row | Source fixture; fictional operations owner |
| closed_tickets | ticket_id, region, minutes; one closed ticket per row | Filter state to closed; omit email; resolution_minutes links to minutes |
| regional_resolution | region, closed_count, total_minutes; one region per row | Count closed tickets and sum minutes; regional_closed_summary links to total_minutes; fictional steward |
T1 and T2 belong to north and contain 60 and 120 minutes. T3 belongs to south with 30 minutes. T4 is an open south ticket with 999 minutes. The executed intermediate relation contains three closed tickets. The final result is north: two tickets and 180 minutes; south: one ticket and 30 minutes.
The saved lineage record connects source minutes to intermediate minutes, then intermediate minutes to final total_minutes. Region carries through both edges. The count mapping records that rows identified by ticket_id contribute to closed_count, while the accompanying rule explicitly identifies COUNT(*). It does not pretend that the output is a renamed ticket identifier.
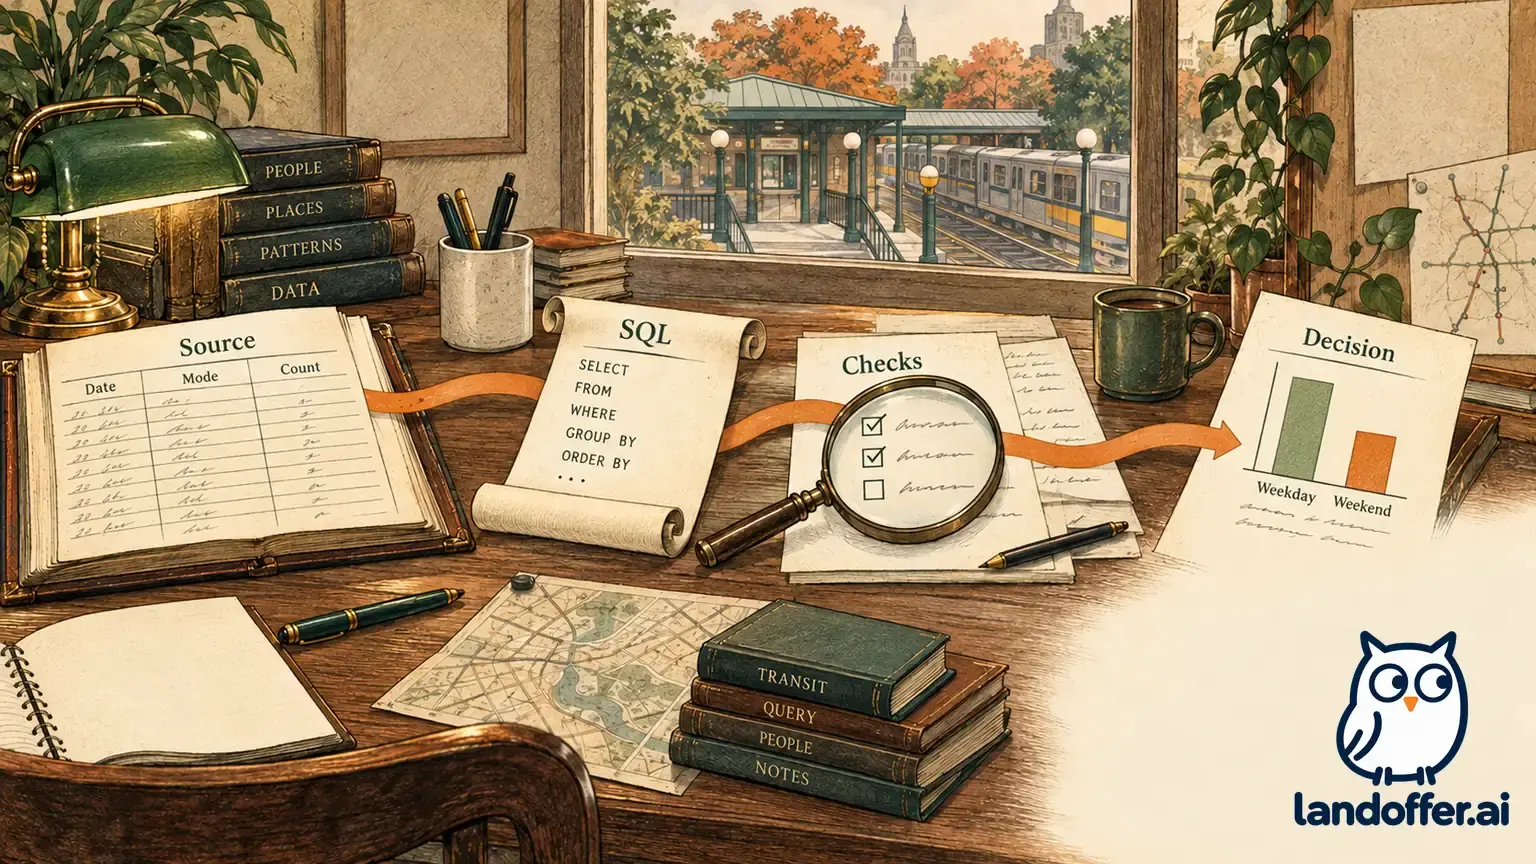
The graph can be read as tickets → closed_tickets → regional_resolution. Each edge includes its transformation rule, so the diagram points to executable evidence rather than standing alone as an architecture claim. Both glossary targets resolve to real catalog columns, every asset owner resolves to a declared role, and all edge endpoints exist.
The verification goes beyond checking spelling. An independent fresh database changes T1 from 60 to 70 minutes: north becomes 190, while south stays 30. Another fresh database changes only the open ticket's minutes to zero; neither regional result changes. These perturbations support the stated dependency and filter for this fixture.
A deliberately invalid mapping attempts to carry email into a target without an email column. The catalog check rejects it. The final relation's schema also confirms that email is not projected. Neither check proves that other identifying information could not exist in a real aggregate, but both expose a concrete inconsistency that a static picture might hide.
Preserve lineage's collection limits
Microsoft's classic Data Catalog lineage guide describes dataset and process relationships, column lineage, manual entries, and source-dependent collection limits. The page is explicitly about the classic catalog and points separately to Unified Catalog asset details. Do not present its classic portal instructions as a tested current Unified Catalog walkthrough.
For your own case, state whether an edge came from executed code, manually maintained metadata, a scanner, or a proposed relationship. Our SQL executed the transformations; our catalog separately declared the edges. Schema checks reject nonexistent fields, while the executed perturbations test the specific closed-ticket dependency. Neither method discovers arbitrary SQL lineage or external consumers.
Retain the SQL beside the graph. If someone changes the filter or adds another consumer, the catalog can become stale even while the database still runs. A sensible next check would compare the revised code, glossary definition, and downstream use before accepting that change. That check has not been implemented as automatic change detection here.
Also record the boundary of the inventory. Three owned local relations are fully listed. There is no evidence about external spreadsheets, copied extracts, dashboards, hidden consumers, or actual production lineage coverage. A small complete scope is more reviewable than an unsupported claim to map every downstream dependency.
Asset two: a completed use request and conditional decision
The second asset is a separately completed request, USE-42, from a fictional capacity analyst. It asks for the three fields in regional_resolution, for capacity planning, for 14 days, without export. Its two signoff fields, manager and steward, are authored Boolean test inputs set to true. They do not authenticate an approver or represent signatures supplied by real people.
The policy evaluator returns conditionally_approved_pending_provisioning. Its completed decision record limits use to that three-column aggregate and stated purpose, sets a maximum 14-day period, requires no export, and records provisioning as false. Its authority field explicitly identifies the signoffs as fictional. No real account, role, database grant, or expiry job is created.
The business rationale is specific: a regional count and total address the stated planning question without adding the source's contact field. That is a proposed minimization choice for the synthetic case, not proof that the result satisfies privacy law or is sufficient for every capacity-planning task.
Five independent counterexamples change one part of the request. A row-level email request is declined for asset and column scope. Marketing reuse is declined for purpose. An export request is declined, a 30-day window is declined, and a missing steward signoff is declined. Each result retains its reasons alongside the altered request, so a reviewer can inspect why it differs from USE-42.
The conditions remain document conditions. The script does not observe what a user does after reading the result, delete files after 14 days, or prevent a copied extract. Its status is deliberately pending provisioning rather than “access completed.” The portfolio's deliverable is a complete review record with explicit unresolved implementation work.
Test the difference between approval and enforcement
The current Purview access-policy documentation distinguishes approval from completed provisioning and explains that asset access must be provided manually or through a configured provider. It also warns that attestations such as no-copy are not enforced by the product. Treat those as important product boundaries, not as behavior tested in this local example.
We ran an explicit counterexample after evaluating a declined contact-data request: a direct SQL query still returned all four synthetic email rows. The SQLite connection had no access-control layer, and the document evaluator did not intercept its queries. The observed result demonstrates that this sample's denial is not a technical barrier.
Preserve that result in the case study. Hiding it would let a reader mistake a policy decision function for authorization enforcement. A real implementation would need the relevant database or platform controls, authorized provisioning, negative access tests, and evidence that expiry and revocation work. Those are proposed follow-up requirements, not completed portfolio achievements.
The same caution applies to approval identity. An implemented workflow would need to verify each actor and their decision authority. The chosen Boolean inputs test only the local evaluator’s branch behavior. Keep requested scope, decision rationale, actor identity, provisioning state, and actual access results as separate records. A single “approved” flag cannot explain all five.
Package the case for an independent review
The bundle includes governance.py, transforms.sql, catalog.json, use-request.json, and both execution results. Run the short command from the output folder:
python evidence/governance.py
Seventeen authored checks passed, and the entire case was reconstructed twice with fresh in-memory databases. The script asserted identical results before saving the replay. This supports reproducibility under the fixture's declared rules. It does not measure catalog adoption, enterprise coverage, or organizational compliance.
Lead an interview explanation with one traceable chain: closed-ticket meaning, the actual state filter, the total-minutes lineage, the permitted planning request, and the lack of implemented provisioning. Then show a counterexample that changed the decision or exposed a limit. That sequence makes the governance judgment understandable without requiring the reviewer to read every line first.
A bounded portfolio claim could say: “Built and executed a synthetic SQLite catalog with glossary-to-column links, checked lineage, a conditional use-decision record, and counterexamples showing that document approval does not enforce data access.” Describe your actual contribution and tools without implying production stewardship or Purview tenant experience.
Before sharing, verify that the bundle contains only synthetic material and that every claimed relationship points to code or a clearly labeled document. Use LandOffer.ai to organize relevant applications, keeping this project’s glossary, lineage, and access-decision evidence beside the responsibilities it actually demonstrates.
Download the worked example files
Download the curated educational companion. Read PUBLICATION-README.md after extraction for the public file layout, replay commands and requirements. The listed offline Python checks were rerun from the extracted archive in a disposable directory. The earlier local report and commands describe the original evidence environment; use the companion README for the portable layout. No whole evidence directory, credentials or compiler binaries are included.
Sources and Further Reading
- Microsoft Purview glossary terms: current public article body read October 23, 2026; business context, term links, and policies.
- Classic Data Catalog lineage guide: current published classic-scope body; lineage mechanisms and collection limits, not a tested Unified Catalog UI.
- Unified Catalog access policies: current public body; approval/provisioning distinction and attestation limitations. No tenant or real approval workflow was operated.