LandOffer
Job search
CISA Exam vs. CISA Certification: Check Audit Experience Before Buying Prep
Two completed fictional experience and timeline records separate CISA learning and passing from verified work, limited waivers and certification approval.
You may take the CISA examination before meeting the certification’s experience requirement. Passing does not make you CISA-certified. Before buying preparation, separate what you need to learn from the work history, permitted waivers, verification and application deadline you would need for the credential.
We checked current ISACA sources on October 23, 2026. The two completed records below are fictional planning exercises, not eligibility decisions or actual applications. No account, exam or purchase was used. Start with recent audit, control and security roles on LandOffer.ai, retain the exact credential requirement, and decide whether preparation addresses the work you want.
Taking the exam and earning CISA are separate steps
ISACA’s certification requirements explicitly allow interested candidates to take the examination before satisfying the experience requirement. Certification adds an application, qualifying work, verification and professional obligations. Paying for learning material changes none of those conditions.
The published baseline is five years of professional information-systems auditing, control or security experience related to the CISA job practice areas. Experience must fall within the ten years preceding the certification application; candidates have five years after passing to apply. The work window is measured backward from application; the application deadline is measured forward from passing.
The application processing charge is US$50, payable after official scores are released. It is not the examination price or payment for automatic approval. ISACA also requires adherence to its professional ethics and auditing standards. Preserve the difference between an exam result, an application being reviewed and certification being awarded when describing your status.
This matters when an employer requires an active credential. A course completion or examination pass cannot silently replace that wording. Conversely, a role that emphasizes control work and treats certification as preferred may warrant a closer look at your actual duties. This guide does not establish that any employer accepts a particular substitute.
Match duties to the current job practice, not just the title
The current CISA outline covers five areas: auditing process, IT governance and management, systems acquisition/development/implementation, operations and resilience, and protection of information assets. Its task statements include evaluating change controls, backup processes, logical access and implementation readiness.
That breadth means relevant work is not confined to a job titled IT Auditor. It also does not mean every month working with a computer qualifies. Identify the system, risk or control, what you personally did, the period and who could verify it. “Worked on production systems” leaves the important part unexplained.
For example, installing an approved patch and evaluating whether a patch-management control operates as designed are different contributions. Both can be important work. Record the actual contribution rather than rewriting the first as the second. If your work concerns control or security, investigate its fit with the stated job tasks; do not assume only independent audit leadership can be relevant.
Describe the task, evidence and responsibility in terms a former colleague could verify. A project can show several responsibilities without becoming several simultaneous years of experience. Keep employment dates and responsibility mapping separate, and avoid attaching confidential client records or live security configurations to a public resume.
Apply the current waiver limits before adding years
ISACA’s current experience FAQ describes a minimum of two years in at least one CISA job-practice domain. Its education section permits only one education waiver. It lists two years for a bachelor’s, master’s or doctorate in any field, and three for an information-systems or related master’s, including listed computing disciplines.
The same FAQ lists a one-year general-work substitution for a continuous year with one organization in information systems or financial auditing; those two categories cannot be combined. The 2026 candidate guide caps total experience waivers at three years. A three-year education waiver therefore leaves no extra waiver year to add.
Do not sum every credential on your resume. In particular, a bachelor’s plus a related master’s is not two education selections. Older application documents found through search can describe different substitution language. Use the current instructions for your application and retain degree evidence for review rather than treating a search result as approval.
Verification is another requirement, not an arithmetic operation. The current FAQ permits an independent person you worked with, including a supervisor, manager, colleague or client; it excludes family and HR. The main certification page directs candidates to supervisor or manager verification. Choose an appropriate verifier under the current instructions, and resolve any uncertainty before submission.
Completed experience record: a control-testing contribution
Asha is a fictional quality engineer investigating an IT-controls career. Her record stipulates eighteen months of deployment support followed by thirty distinct months of control-related work, January 2024 through June 2026. She also has a completed computer-science master’s and an earlier bachelor’s. None of these records has been checked by ISACA.
Her finished responsibility ledger describes the thirty-month role without adding the same months repeatedly:
| Work item | Supplied contribution | Mapping and evidence boundary |
|---|---|---|
| Release approvals | Compared selected releases with required approval records and documented exceptions | Proposed change-control relationship; test scope and reviewer retained |
| Access reviews | Checked that sampled access removals matched approved requests | Proposed logical-control relationship; did not own all identity operations |
| Restore evidence | Compared scheduled restore-test results with the documented recovery requirement | Proposed resilience relationship; did not run every restore |
| Exception follow-up | Recorded owner responses and supplied unresolved items to the reviewer | Follow-up contribution; no claim to have issued an independent audit opinion |
| Eighteen earlier support months | Installed releases under approved instructions | Keep eighteen months separate; the supplied facts do not establish control evaluation |
| Calendar and verifier | Thirty distinct months; former testing supervisor identified in the fictional record | Obtain current verification; three work items do not create ninety months |
Her evidence note specifies the period, testing purpose, selected population, her comparison steps, exception record and reviewer. It describes an access-removal test without supplying user names or screenshots. It distinguishes the conclusion she documented from the reviewer’s responsibility for the broader assessment. This is a completed description of supplied facts, not a test performed for this article.
Her waiver calculation selects the related master’s category for investigation: thirty months of proposed qualifying work plus thirty-six months of potential education substitution equals sixty-six months. It excludes a second twenty-four-month bachelor’s waiver and any additional general-work waiver. Thirty supplied work months exceed the twenty-four-month minimum before substitution, provided ISACA accepts the work.
That arithmetic is conditional. The degree category, duties, dates and verifier still require acceptance. Asha’s ledger does not turn a computing degree into audit work, nor does it decide whether her earlier support period qualifies. It simply prevents her purchase plan from depending on duplicated time or stacked education allowances.
Her completed decision reads: “Review CISA preparation against the current control and assurance topics. My strongest application evidence is the thirty-month testing role, subject to verification. Use only one education category and preserve ISACA’s approval step. Do not describe myself as CISA-certified because I bought preparation or can reconcile a planning ledger.”
Completed timeline: an exam pass has several boundaries
Damon is a different fictional candidate. He stipulates four years of qualifying work from November 2022 through October 2026, a bachelor’s degree and a passing examination dated October 15, 2026. The dates are invented inputs; no score report or employment record was inspected.
His completed plan uses a December 1, 2026 application-review checkpoint and a February 1, 2027 submission target. These are his chosen planning dates, not ISACA processing commitments.
| Clock or condition | Filled planning entry | Resulting action |
|---|---|---|
| Exam registration eligibility | Hypothetical registration record displays May 1–November 1, 2026 | October 15 sits inside the supplied window; retain the actual account deadline if registering |
| Passing result | Stipulated October 15, 2026 pass | Await official result before application payment and submission |
| Five-year application window | Track the October 2031 five-year boundary from the pass | Target February 2027 instead of depending on the last possible day |
| Ten-year work lookback | Review on December 1, 2026 | Retain November 2022–October 2026 work; do not add unrelated 2014–2015 employment |
| Work plus one education category | Forty-eight supplied months plus twenty-four potential months | Seventy-two planned months, still subject to work and degree verification |
| Verification and designation | Former manager identified; approval not yet granted | Keep certification pending and retain evidence before submitting |
The older employment is outside the ten-year lookback at his checkpoint. Waiting changes that boundary: a work period does not remain eligible indefinitely merely because it was on the resume when he passed. Damon will recalculate using the actual submission date and current rules if his plan slips.
His completed fee worksheet reserves $760 for a nonmember examination and $50 for a later certification application: $810 for those two separate items. It excludes preparation, tax, rescheduling, retakes, membership and maintenance. An exam pass is a stipulated case input, not evidence that Damon actually paid either charge.
His status note reads: “Examination pass supplied for planning; certification has not been awarded. Collect manager verification and degree documentation, check the rolling experience window at submission, and submit well before the five-year limit. Do not use CISA as an earned post-nominal while approval is outstanding.” No application or message was sent.
Buy the preparation scope you actually need
ISACA’s CISA overview lists examination registration at $575 for members and $760 for nonmembers. The $185 difference is not automatically a membership saving after dues and other charges. Compare actual membership cost and benefits separately; nonmember pricing itself shows that membership and examination registration are different purchases.
The current examination has 150 multiple-choice questions and four hours. The candidate guide uses a 200–800 score scale with 450 required to pass; do not convert that threshold into a percentage-correct promise. Registration normally provides six months to take the examination, a different period from the five years to apply after passing.
The guide says examination fees are nonrefundable and nontransferable. Preparation access also has its own term: the overview advertises a six-month question-database subscription. That subscription is not a second six-month exam window or an experience waiver. Check the edition, taught topics, access period and included registration before paying; each determines what the purchase covers.
Asha would compare material on selecting evidence, evaluating controls and communicating findings. Damon would separately check any remaining knowledge gap despite his stipulated pass. Neither needs a blanket bundle merely because several products share the CISA label. No paid course content or practice-question quality was tested for this guide.
Include the obligations after certification
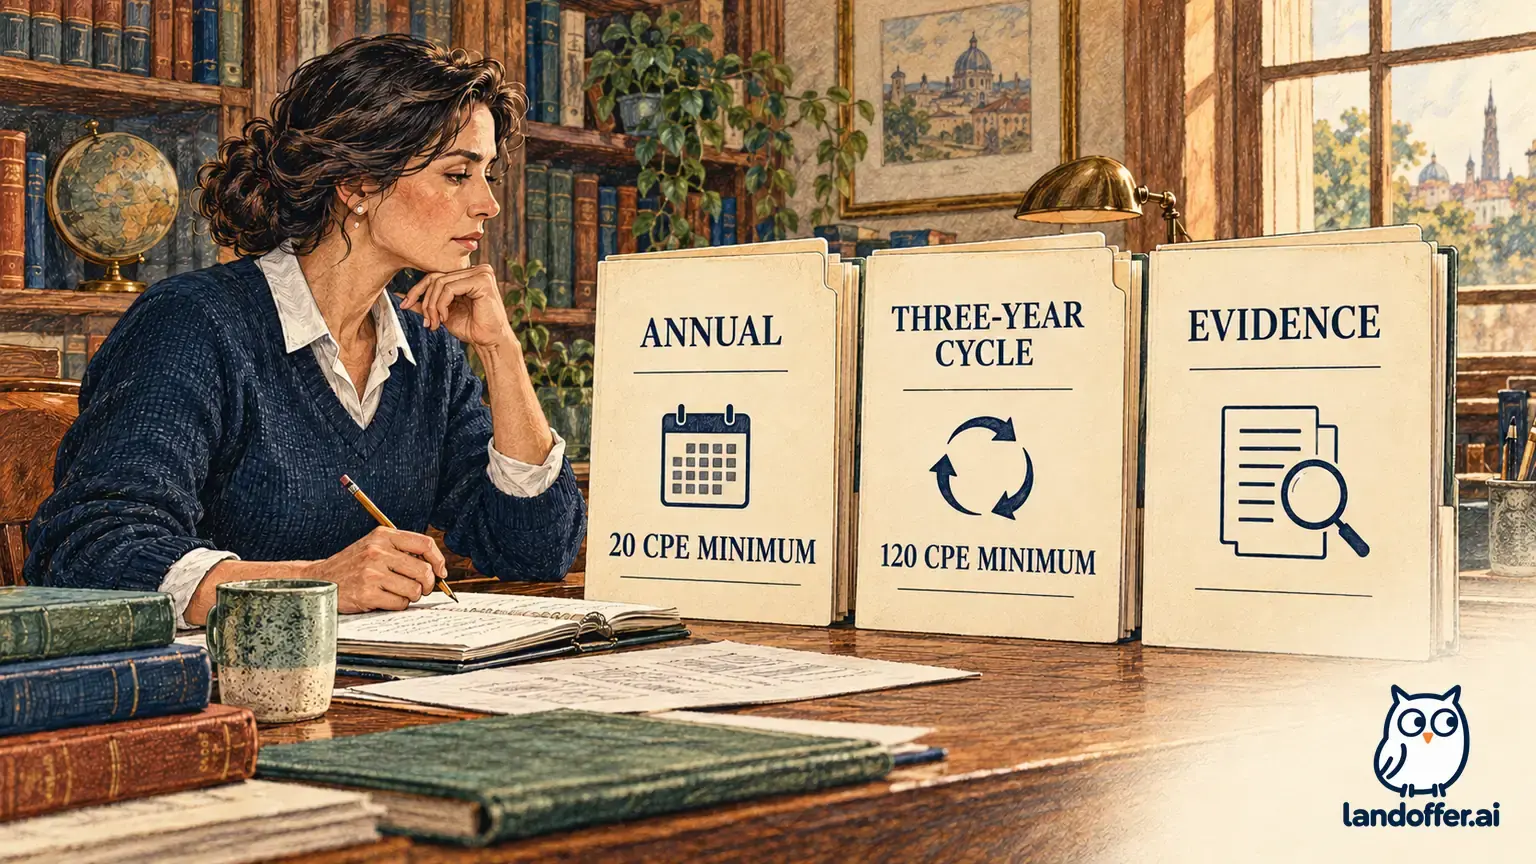
The maintenance rules require at least twenty CPE hours each year and 120 over a three-year reporting period. Annual maintenance is $45 for members or $85 for nonmembers. These fees are separate from membership dues, the exam and the application charge.
A fictional future plan of thirty, forty-five and forty-five relevant CPE hours totals 120 and exceeds the annual minimum in each year. A plan of zero, sixty and sixty reaches 120 but fails the yearly minimum. These are arithmetic illustrations, not earned hours or a determination that an activity is reportable.
Keep qualifying activity documentation and report accepted hours under the actual policy. Maintaining the designation involves ethics, auditing standards and potential CPE verification as well as paying a fee. Purchase decisions should account for that continuing work without treating payment as proof of compliance.
Decide what preparation would change
Before spending, finish a responsibility ledger, select only allowed substitutions, record the relevant dates and identify a suitable verifier. Then define the knowledge gap a specific preparation resource would address. If the work record remains uncertain, resolve its scope and verification before relying on certification as the expected result of preparation.
Return to recent LandOffer.ai openings with the employer’s exact requirement beside your current status. Describe verified work and earned credentials accurately. A preparation purchase can address learning needs; ISACA controls certification approval, and the employer controls its hiring decision.
Sources and Further Reading
- ISACA: earning CISA, application and experience windows
- ISACA Support: current experience, waiver and verifier details
- ISACA: current CISA job-practice outline
- ISACA: current examination and preparation overview
- ISACA: 2026 certification examination candidate guide
- ISACA: CISA maintenance and CPE requirements