LandOffer
Job search
TryHackMe vs. HTB Academy: Compare Guided Labs for Your First Security Role
Compare guided SOC learning routes, foundation needs, current Academy access subscriptions and TryHackMe plan boundaries through two completed candidate decisions.
Compare TryHackMe and HTB Academy using three concrete inputs: the security task you need to practice, what you already know and the access plan for that content. TryHackMe offers a broad foundations route and a named SOC Level 1 path. HTB Academy offers a SOC Analyst path with a separate prerequisites sequence. Neither a subscription nor a completed path establishes that you can perform a first security role without further evaluation.
LandOffer publishes this comparison and offers a place to browse recent roles before choosing training. We reviewed public provider pages on October 23, 2026. We did not create accounts, launch machines, complete paid labs, buy exams or assess teaching quality. This comparison covers documented guided learning, not the full HTB product family. The candidates, role briefs and completed work examples below are fictional.
Start with a first-role task rather than a platform ranking
A junior SOC role can require reading alerts, examining logs, explaining uncertainty and handing an investigation to another analyst. A junior penetration-testing role asks for different evidence. Read the actual duties before buying a subscription because the platform is associated with “hacking.” A familiar brand cannot decide which of those activities fits your target.
For this comparison, use one constructed SOC brief: inspect an alert, identify relevant event evidence, write a concise triage note and explain when to request more information. The brief is an editorial teaching input, not a current employer posting or a universal SOC hiring rubric.
Then assess your starting point honestly. Someone who cannot yet explain an operating-system log needs a different next lesson from someone who manages Windows systems but has never written an investigation report. Both might be preparing for a first dedicated security job.
Decide what you will study next and what evidence you will be able to explain afterward. Catalog size, streaks and difficult-sounding module names are weak substitutes for that decision.
Compare the documented routes on the same criteria
TryHackMe's Cyber Security 101 outline covers networking, Linux, Windows and Active Directory foundations alongside introductory offensive and defensive topics. Its SOC Level 1 outline names alert triage and reporting, SIEM tools, endpoint monitoring and network analysis. Those are curriculum descriptions, not results from our own completed labs.
HTB Academy's SOC Analyst preview lists modules such as Incident Handling Process, Security Monitoring & SIEM Fundamentals, Windows Event Logs and investigation with Splunk. It points learners toward SOC Analyst Prerequisites, which covers foundational operating systems, networking and related subjects.
| Criterion | TryHackMe route to inspect | HTB Academy route to inspect | Your decision question |
|---|---|---|---|
| Foundation gaps | Cyber Security 101 | SOC Analyst Prerequisites | Which named topics can you already explain independently? |
| SOC work | SOC Level 1 | SOC Analyst job-role path | Which lessons match the alert, evidence and reporting work you need? |
| Learning unit | Named rooms organized into a path | Named modules and sections organized into a path | Can you protect time for a useful sequence rather than random activity? |
| Demonstration | Explain a completed practice investigation | Explain a completed practice investigation | What did you decide, what evidence supported it and what remained unknown? |
The last row is deliberately the same. Your employer-facing explanation needs evidence regardless of where you learned. We have not established that one platform produces better reports, more transferable skill or a higher hiring rate.
Worked choice: Mina needs foundations before a SOC specialization
Fictional case: Mina works in customer support and is exploring a junior SOC role. She can describe an escalation ticket but cannot yet distinguish a network connection from an authentication event. In this fictional scenario, she has four weekly study sessions available and wants a guided starting sequence.
She completes this gap record against the constructed SOC brief:
| Required practice | Mina's stipulated starting point | Chosen next work | Evidence she plans to produce |
|---|---|---|---|
| Interpret a basic log | Has not worked with system logs | Inspect operating-system and logging foundations first | Explain the fields in a synthetic event without copying a walkthrough |
| Relate network and account activity | Mixes the two in her notes | Work through relevant networking and defensive fundamentals | State which observation concerns a connection and which concerns sign-in |
| Triage an alert | No prior analysis method | Continue toward a SOC-focused sequence after the foundations | Write a short note separating observation from suspicion |
| Communicate a handoff | Familiar with support tickets | Reuse concise communication skills while learning security context | Ask a specific next question instead of asserting compromise |
Mina chooses TryHackMe's foundations route as her first investigation because its published sequence matches the introductory concepts she needs. She samples accessible material before choosing a paid plan. HTB Academy remains a viable alternative if its prerequisites format suits her better; she has not tested either paid learning experience.
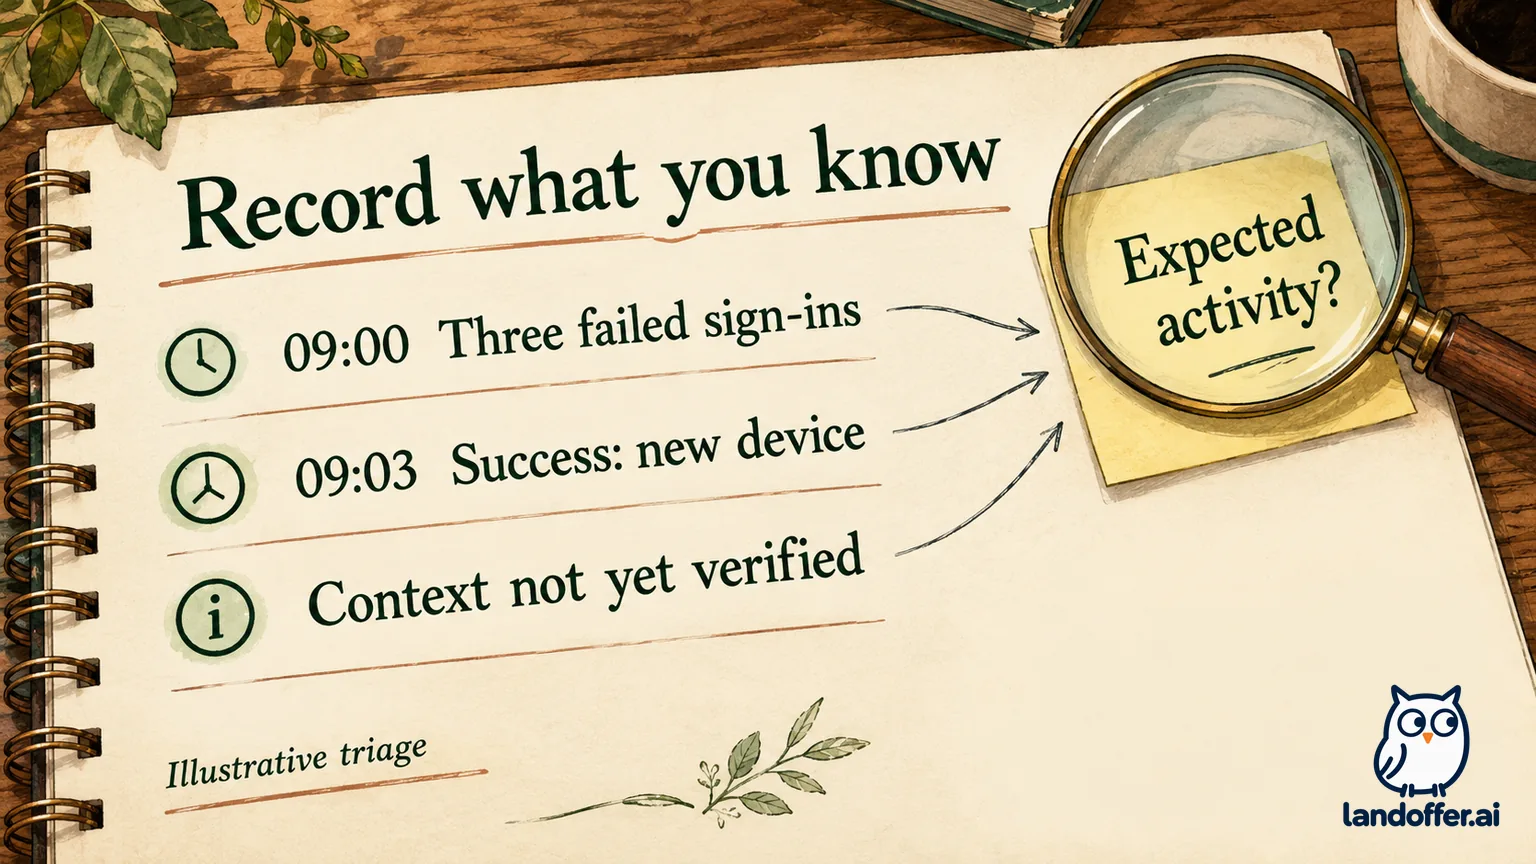
Her completed fictional practice note uses three invented events: three failed sign-ins at 09:00, a successful sign-in from a newly recorded device at 09:03, and no available user-verification note. She records the sequence and asks whether the activity was expected. She does not label the account compromised from those facts alone.
The note is an example of bounded reasoning, not a TryHackMe lab answer or operational detection rule. Her next learning need is visible: understand the available log context and how an analyst would request corroborating information. A completion badge would not supply that reasoning for her.
Read today's access rules instead of an old Cube budget
HTB's pricing-change announcement moved monthly Silver, Gold and Platinum from recurring Cube allocations to tier-based access starting October 12, 2026. Search results still surfaced an older US$18 Silver plan with 200 monthly Cubes during this review. That indexed description does not match the current page body.
The current Academy subscription guide lists Silver Monthly at US$30, with access through Tier II and the SOC Analyst path. Silver Annual is US$550 with additional benefits including two specified voucher inclusions. Academy and HTB Labs subscriptions are separate. These are published prices, not authenticated checkout totals.
For the new access model, the guide says completed modules remain available for reading and review after expiry, excluding step-by-step solutions. Do not turn that into permanent access to every module you merely opened. Keep the current plan and completion status together when planning later revision.
If an older account has a transition offer, use its actual billing record and the provider's current terms. This comparison does not establish an individual renewal price. A cheaper historical screenshot should not become a promise about what a new subscription costs today.
Check TryHackMe's Premium and MAX boundary
TryHackMe's current pricing page distinguishes Free, Premium and MAX. Free lists free rooms and a one-hour daily AttackBox limit. Premium lists beginner learning paths and unlimited AttackBox; MAX adds advanced paths and broader room access. Inspect the particular path and room entitlement instead of reusing older advice that treats every paid feature as one undifferentiated Premium product.
Our public pricing render displayed euros, including an annual-billing monthly equivalent. We did not verify a U.S. checkout quote. This article therefore does not rank TryHackMe as cheaper or more expensive than Academy by mixing that display with Academy's USD table.
A monthly-looking annual figure also does not establish that you can pay for only one month at that rate. Record the actual charge due, billing period, tax and renewal terms before choosing so a monthly-looking label does not hide a larger payment commitment. Compare equivalent access for the content you plan to use, not a free sample on one side against a broad paid subscription on the other.
The ability to open a browser environment can reduce setup work, but it does not establish that the teaching format fits you. For a first purchase, choose a small learning objective you can evaluate before extending the commitment.
Worked choice: Noah needs SOC investigation practice and a bounded budget
Fictional case: Noah is a junior systems administrator preparing for his first security-specific role. He already works comfortably with Windows, Linux and networking in this invented history. His gap is explaining a log-based investigation and writing a defensible handoff. He has a US$100 training limit for an initial two-month period and no exam requirement in his constructed target brief.
He compares the published HTB SOC module list with the TryHackMe SOC outline. Both contain relevant investigation topics. He selects Academy's SOC Analyst route because the named incident-handling, event-log and SIEM modules form a specific sequence he wants to investigate, not because we proved it is more advanced or better taught.
His completed purchase record is:
| Decision item | Noah's completed record |
|---|---|
| Training objective | Explain one synthetic alert investigation and a handoff, with evidence and uncertainty |
| Initial Academy access budget | Two US$30 monthly periods = US$60 before tax or other charges |
| Remaining stipulated allowance | US$100 − US$60 = US$40; not a prediction of checkout tax or required study duration |
| Annual alternative | US$550 exceeds this initial budget, despite additional benefits |
| Exam decision | No exam purchase now; no requirement or readiness established |
| HTB Labs | No separate purchase justified by this Academy learning objective |
| TryHackMe alternative | Keep its SOC outline as an option; obtain the actual applicable quote before a cost comparison |
Noah's final note says: “Start with a two-period Academy allowance if the current checkout fits the limit. Review learning progress before another renewal. Defer a voucher purchase until an examination serves the target role and the study schedule supports it.” Two months is his budgeting assumption, not a provider completion estimate.
If he remains dependent on step-by-step guidance after the first period, the answer is to reassess the learning sequence. Buying a larger catalog does not itself fix the missing independent explanation. If the format does not fit, he can compare a specific TryHackMe room before switching rather than paying for both indefinitely.
Keep path completion, examinations and job evidence separate
TryHackMe's credential guide distinguishes learning-path completion from professional certifications such as SAL1, which require a practical examination. Buying learning access or finishing a path is not the same as passing that separate assessment. Record the credential you actually earned rather than promoting progress into a qualification.
Apply the same discipline to Academy. An access plan can include a voucher benefit without establishing that you meet the chosen exam's requirements or have time to use it. Inspect that examination's current instructions before assigning the voucher value in your own budget.
For an application, explain the bounded work: the training context, the evidence you examined, the decision you made and its limitations. Do not describe a simulated lab as employment, a production incident or authorization to test an unrelated system. Neither Mina nor Noah needs to invent a customer outcome to discuss a useful practice artifact.
Choose TryHackMe first when its named foundation sequence addresses your starting gaps; choose Academy when a specific guided module sequence and its current access terms fit your objective. If your current platform already supplies the work you need, finishing that sequence may be more useful than switching brands. Write down one training artifact you can explain independently, then browse recent roles on LandOffer.ai and compare your evidence with actual duties. Neither platform nor LandOffer guarantees a first security job.