LandOffer
Engineering Practice
Create an SBOM That Can Answer Which Release Contains a Dependency
An executed synthetic release-inventory query traces an exact transitive component version, distinguishes a scoped negative from missing inventory, and rejects mismatched artifact or SBOM digests. The completed triage record keeps applicability and deployment checks open.
An SBOM can answer which release contains a dependency when its component identities and versions are tied to a specific release artifact, and its dependency relationships remain queryable. Retain the release reference, the exact artifact digest, the SBOM digest and the inventory’s declared scope together. Finding a component is a starting point for security review; failing to find it in an incomplete inventory is not evidence that the release is unaffected.
This LandOffer.ai guide creates two small authored release inventories and queries them with an isolated Python example. The product, components and advisory are fictional. JSON, digest and graph checks were actually executed; no package was installed, vulnerability feed consulted, real binary scanned or production system changed. The example demonstrates traceability within its stated records, not a security certification.
Decide what the inventory describes
The CMS SBOM overview, last reviewed June 20, 2023 and checked October 28, 2026, describes component, version and license information as support for software transparency and vulnerability tracking. It also emphasizes completeness, quality and the tooling that consumes the inventory. That overview is context, not a claim that this example satisfies a current federal procurement requirement.
Before generating an inventory, name its subject. Is it source before a build, a resolved application package, a container image, or an installed system? A source manifest can describe intended dependencies without accounting for everything in the packaged artifact. A container inventory may include operating-system packages that an application-only record lacks.
Record the lifecycle stage and coverage that your collection method can support. Include direct and transitive components where the chosen method can identify them, and document exclusions. Do not label an inventory complete merely because it is valid JSON or has a large number of rows.
For the fictional Beacon service, the exercise covers two listed application libraries in each authored release record. It excludes operating-system packages, build tools, plugins loaded later and actual runtime discovery. The accompanying “artifact” is a small text fixture listing those components, not an executable distribution. This limited subject makes the demonstrated checks reproducible without pretending that a text inventory inspected a real application.
Use identities and relationships that survive a name search
CycloneDX’s software-dependency guidance explains direct and transitive relationships through unique document references, ref and dependsOn. It cautions that a component omitted from the dependency graph can have unknown dependencies; omission does not establish that it has none. Its current page illustrates version 1.7.
This exercise deliberately pins the older CycloneDX 1.6 JSON schema as its field reference. It uses the format/version fields, a subject component, component references, versions, hashes and dependency entries from that schema. Version 1.6 is the example’s chosen format, not a claim that it is the newest specification or required by every consumer.
Choose a format and version your actual producer and consumer support. Validate against that exact schema, then check semantic relationships separately. A document can meet structural rules while describing the wrong release, omitting a packaged library or joining two different components by an ambiguous name.
The fictional libraries use generic package URLs, such as pkg:generic/comet-parser@1.4.0. They are not claims that an npm, Maven or other public package with those coordinates exists. In real work, preserve the relevant ecosystem, namespace, package identity and resolved version; treat an advisory-to-component match as a mapping decision, not an arbitrary substring search.
Completed inventory: two releases and one missing record
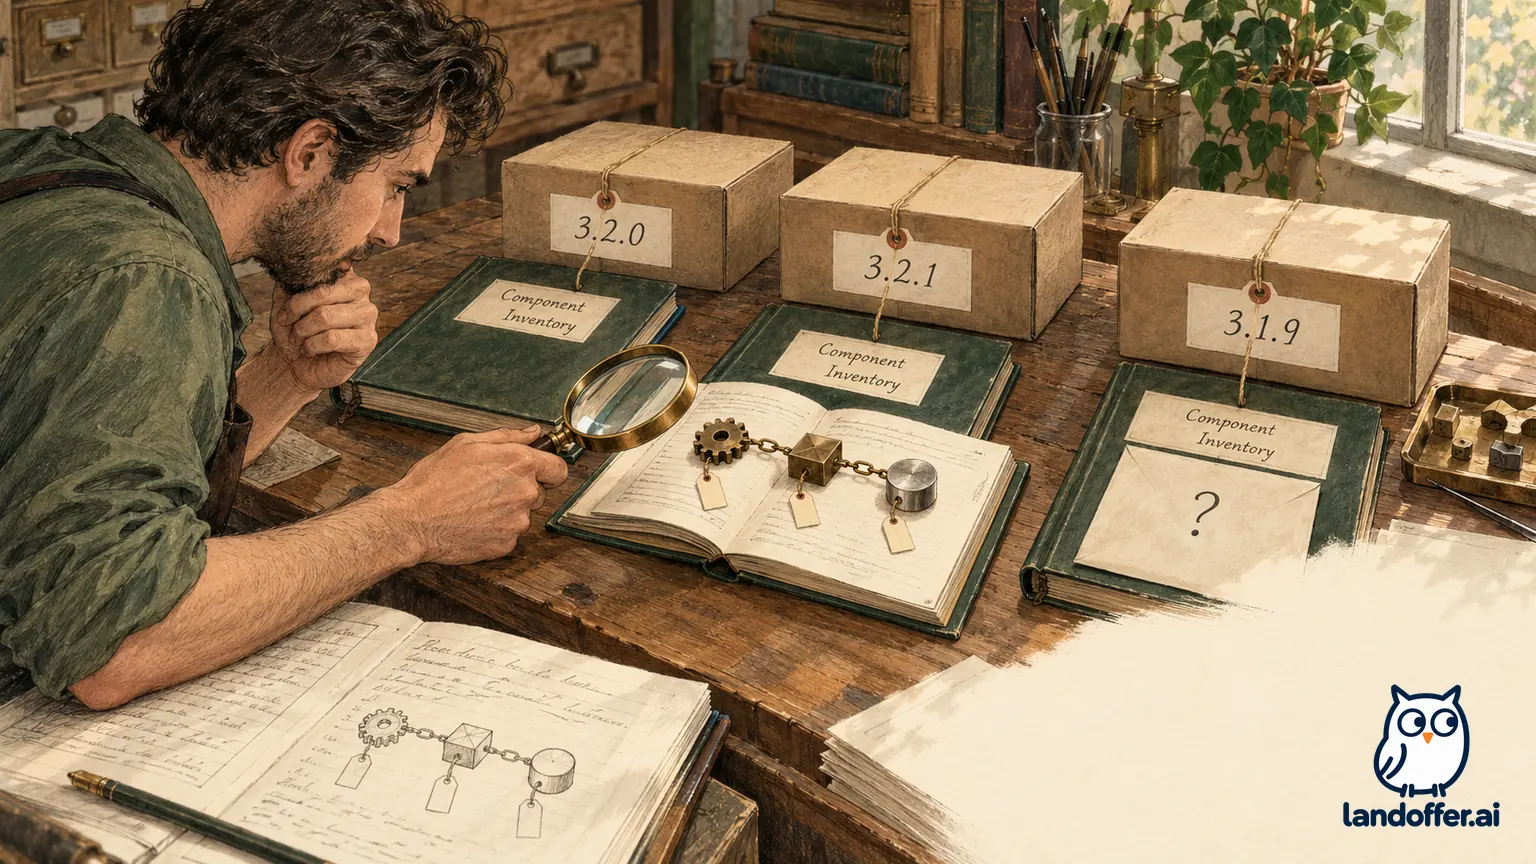
Beacon 3.2.0 lists orbit-core 0.8.0 as a direct dependency. That component depends on comet-parser 1.4.0. Beacon 3.2.1 retains the same core version but lists parser 1.5.0 underneath it. A third release, 3.1.9, has no retained inventory in the exercise.
The following table is the filled component and relationship record. Each parser has an explicit empty dependency entry within this authored scope. It is not silently omitted from the graph.
| Release subject | Component identity and version | Relationship recorded | Scope and evidence |
|---|---|---|---|
| Beacon 3.2.0 | orbit-core 0.8.0 |
Directly required by Beacon 3.2.0 | Listed in the authored text artifact and its JSON inventory |
| Beacon 3.2.0 | comet-parser 1.4.0 |
Required by orbit-core; transitive from Beacon | Listed parser node, with no further dependencies in this fixture |
| Beacon 3.2.1 | orbit-core 0.8.0 |
Directly required by Beacon 3.2.1 | Separate artifact and separate inventory retained |
| Beacon 3.2.1 | comet-parser 1.5.0 |
Required by orbit-core; transitive from Beacon | Different exact parser version, not a relabeled copy of the earlier inventory |
| Beacon 3.1.9 | Unknown | No relationship evidence available | Missing inventory; no negative component conclusion |
The example leaves license assertions out rather than inventing licenses for nonexistent packages. A real SBOM process must collect the relevant license information and distinguish what the supplier declares from what your collection method establishes. Missing information needs a visible follow-up; a plausible-looking value is not a substitute.
A release index connects each text artifact to its own JSON record and stores both SHA-256 digests. For 3.2.0, the actual artifact digest begins 2c21915eaaec; for 3.2.1, it begins 4a99ccf6bd76. These shortened prefixes are labels for the article. The retained index and checks use the full digests, not prefix matching.
The subject component’s recorded artifact hash must agree with the release index, and the file being inspected must produce that digest. The inventory’s own digest is separate, so the reviewer can identify which of the two files failed its binding check. Confusing those two hashes would leave the team unable to tell whether the application artifact changed or the accompanying inventory changed.
Hash agreement establishes consistency between these local records. It does not authenticate the supplier, prove that the artifact contains every listed component or establish trustworthy provenance. An attacker or mistaken process could replace both an artifact and an unsigned index. Use the organization’s approved authenticity and provenance controls in addition to this binding check.
Run a specific containment question through the records
The authored notice SIM-2026-01 asks the team to locate the exact version comet-parser 1.4.0. Its identifier and exact-version condition were authored for this exercise; it is not a real CVE, vulnerability disclosure or published affected-version range. No conclusion about an actual parser follows from its invented description.
The isolated query first checks the retained SBOM digest and the artifact binding. It parses the component records, checks that references are unique and that graph targets exist, then walks from the release subject to the requested component and exact version. It does not infer dependency presence from the name of the application or from an unrelated lockfile.
The actual result is:
| Release checked | Observed output from the fixture | Meaning and next action |
|---|---|---|
| 3.2.0 | contains-listed-version; path beacon-3.2.0 → orbit-core-0.8.0 → comet-parser-1.4.0 |
Listed transitive containment found; send this release and path for advisory assessment |
| 3.2.1 | not-found-in-stated-inventory for parser 1.4.0 |
The retained inventory lists parser 1.5.0; this is a scoped negative for that exact query, not an all-vulnerability clearance |
| 3.1.9 | unknown-no-inventory |
Obtain or reconstruct the correct inventory before drawing a containment conclusion |
The path matters because it tells the maintainer where to investigate the dependency. Looking only at direct dependencies would find orbit-core and miss why the parser is relevant. In a larger graph, retain every relevant path or explain why your query returns only one; this small fixture has one path to the target.
The Python 3.12.14 run also exercised two deliberate failures. An incorrect SBOM digest returned invalid-sbom-binding; an incorrect artifact digest returned invalid-artifact-binding. Neither case was reported as “dependency not found.” A shortened name, comet, did not match comet-parser, and a separate query found parser 1.5.0 in 3.2.1.
These checks cover the fixture’s graph, exact matching and local bindings. They do not implement a general advisory-range parser, verify package-manager resolution or perform full CycloneDX JSON Schema validation. The retained JSON and field inspection therefore should not be represented as a successful schema-validator run.
Complete the triage record without calling containment a fix
Fictional release engineer Marin and security reviewer Ellis use the query to complete a triage record. Marin attaches the full artifact and inventory digests, the exact query, the graph path and the declared coverage to case B-24. Ellis owns the applicability assessment, Marin owns the inventory/path evidence, and Pia owns the archived-release gap; none records the release as exploitable or cleared.
For 3.2.0, Ellis records “listed version present; applicability review pending.” The next question is whether the notice’s actual component identity, affected conditions and usage apply to the artifact. In a real investigation, configuration, vulnerable functionality and deployment context may matter. Presence alone does not answer those questions.
For 3.2.1, Marin records the parser version shown by the inventory without calling the release patched. The example has not established that 1.5.0 fixes a real issue, that the record is complete beyond its two libraries, or that any environment runs 3.2.1. A different version number is evidence about inventory content, not proof of remediation.
For 3.1.9, release owner Pia owns the missing-inventory follow-up. The release stays “unknown,” and Pia must identify the correct archived artifact and an authorized collection method. Generating a new inventory from the current source branch would not necessarily describe that old release. If reconstruction cannot establish adequate coverage, retain that uncertainty in B-24.
The resulting handoff separates three tasks: containment is documented for the fixture; advisory applicability is still pending; deployed-release identification is not yet available. Nobody closes the case on the strength of the SBOM query. No real security incident, notification, upgrade or customer communication occurs in this example.
Keep the record useful after the first query
Generate and retain the inventory as part of the relevant release process so it travels with the artifact it describes. Save the producer, producer version, generation inputs, chosen SBOM format and scope, along with the release and digest references. Review permissions before distributing internal inventory information; package lists and supplier details may reveal information your organization controls.
When a release is rebuilt or repackaged, reassess its artifact identity and inventory rather than reusing a filename that happens to contain the same version text. If you correct the inventory without changing the artifact, preserve the prior record and identify the replacement clearly. Keep inventory revisions distinct from application-release versions.
A useful operational question is not only “Can we generate an SBOM?” but “Can a reviewer trace this advisory candidate to an exact artifact and identify where the record is incomplete?” Exercise that question on an authorized sample before relying on the workflow during an incident. Compare the inventory’s collection scope with the packaged artifact even when parsing succeeds.
Related workplace guides are available from LandOffer.ai. Start the next review with one release artifact, its retained inventory and a specific component query. Record which of the four states the query produced: containment, scoped absence, unknown coverage or invalid binding. Assign the applicability and deployed-release checks to named owners before calling a dependency issue resolved.
Sources and Further Reading
- CMS: Software Bill of Materials — component information and inventory-quality context; last reviewed June 20, 2023; checked October 28, 2026.
- CycloneDX: Software Dependencies — reference-based direct and transitive dependency graphs, including unknown dependencies; current examples use 1.7.
- CycloneDX: Version 1.6 JSON Schema — pinned field reference for the authored JSON fixture; structural field inspection is separate from full schema validation.